



In the manufacturing realm, employees are often remotely located on a factory floor, a logistics or warehousing center, or in the field.
Document control is the cornerstone of quality, compliance, environmental health and safety (EHS) and process excellence. Quality process information, work instructions, job descriptions, and specifications must all be created, revised, distributed, tracked and “retired” with consistency and efficiency. While other elements of the corporation are working on various stages of automation and digital transformation, the quality department and the documents that fuel the organization remain mired in manual (or email-aided) processes.
This situation can be remedied with automation, too, but first it’s important to consider the backdrop of what makes effective document control and how it can drive operational excellence. Let’s look at ten elements to keep top of mind when considering deploying an automated document control system.
No two document types are alike, clearly. For instance, a job description has different review and approval process steps that involve different people and departments than does a work instruction or engineering specification.
A document control system designed around best practices will allow you to configure dedicated workflows for different document types and personalize the entire document cycle. A flexible solution lets you build the document control system around your processes, rather than having to adapt your processes to the requirements of a piece of software.
Another critical aspect of document control is the ability to segment metadata, or high-level information that describes each document. Examples of metadata include information on a document’s:
Metadata is important for tasks like categorizing, reporting, searching and filtering documents. A system that lets you include metadata based on document type allows you to create unique fields, categories, keywords and more. These configurable forms are essential to optimizing your document control system to meet your organization’s unique needs.
Word, Excel and PowerPoint are the standard for creating documents in most companies today. That’s why you want to look for a document control system that works well with Microsoft Office. When these systems are integrated, any changes you make in a document control form will sync with the associated Office file (and vice versa) while preserving metadata. This linkage ensures consistency between files which eliminates costly and time-consuming version control errors.
A good document control system does far more than serve as a gatekeeper for checking documents in or out of a virtual library. You also need a controlled process for review, approval and distribution according to the workflow you’ve configured for the specific document type.
Flexible routing options are a necessity, as are intelligent business rules that eliminate inefficiencies and bottlenecks in the process. What specifically should you look for?
Critical to any automated document control system is the ability to train your workforce on any changes to documents, such as procedures and specifications. During document creation and revision, you should be able to specify the type of training associated with the document and link new requirements to the employee training system.
A flexible document control system integrated with employee training lets you automatically:
Some companies put documents in a holding pattern before releasing them, allowing employees to undergo training while documents are awaiting release. This process ensures employees are knowledgeable about the new document when it goes live. Some systems even allow you to create tests to verify that people understand the updated documents.
A good document control system does far more than serve as a gatekeeper for checking documents in or out of a virtual library.
Given the inevitable document changes that are routinely required, change request and revision control both need their own customized workflows. These processes are all about driving consistency, efficiency and control to ensure:
If your organization has a tremendous number of documents and associated data within its system, you need flexible tools that help you visualize, streamline and share that data.
The ability to filter documents based on metadata—as noted previously—is only one important capability. Built-in reporting engines that let you create ad-hoc or scheduled reports on the health of the document control system are also important. Not only does this keep people on track with overdue documents, it simplifies administrative tasks like reporting and record-keeping, so that quality professionals can focus on the strategic priorities that matter most to their organization.
Data and document security are fundamental to compliance and process excellence. You need to make sure that only appropriate levels of personnel can access, approve, review and revise key documents.
Your document control system should make it easy to configure viewing, edit and approval permissions for individual users or groups. By making documents available on a need-to-know basis, you can be sure that your team is working efficiently, safely and securely, even in multi-site organizations.
With the increased prevalence of mobile devices in the workplace, many QMS applications now offer mobile document control capabilities. In the manufacturing realm, employees are often remotely located on a factory floor, a logistics or warehousing center or in the field. In situations like this, a document control system that works the same way on the mobile device as it does on a workstation brings a tremendous advantage.
Once approved, most documents should not be altered without going through the defined change request process. By converting attachments from Word or Excel to PDF, you can reduce the likelihood that users will download an editable attachment and modify it on their own. Your document control system should also keep the original, editable attachments hidden and secure for your subject matter experts to easily access as part of the change request process.
The document control system is a central hub for the information that drives your quality system. It is the foundation for compliance and continuous improvement and provides a single source of truth for the policies, practices and regulations that drive your QMS and EHS initiatives.
An effective document control system:
Backed by an integrated QMS, these capabilities deliver a powerful platform for process excellence, unleashing new opportunities to drive your business forward.
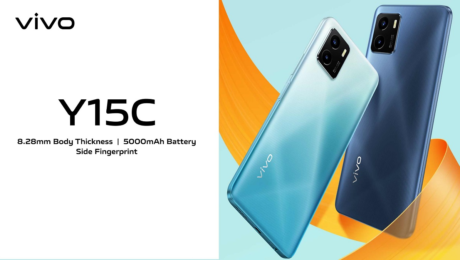
vivo, the leading global smartphone brand, announces the launch of the newest member in the Y series, vivo Y15C in Pakistan. With the launch of the Y15C, vivo furthers its vision of catering to the youth with ‘feature-rich smartphones’ and delivering meaningful innovation across different price ranges.
Ensuring a seamless entertainment experience, the Y15C features a 6.51-inch Halo FullView™ Display with Eye Protection*. The all-new vivo Y15C has been designed to fit the lifestyles of the young consumers who are always ‘On the Go’ and want a powerful handset to keep them going throughout the day.
New Age Camera for Superior Clicks
The 13MP AI Dual Camera on the back, coupled with an f/2.2 large aperture, reveals minute details in the frame and ensures that the subject is always glowing up, thus delivering an elevated photography experience to users. It is supported by a wide range of features to capture any scenario in the full effect of clarity.
Y15C presents Face Beauty, Photo, Video, Live Photo, Time-Lapse, Panorama, Documents and Pro Mode to ease the everyday shooting experience. Additionally, it comes with a 2MP Super Macro Camera on the back that offers a 4cm focus, which helps to discover tiny and exciting worlds full of gems hidden from naked eyes.
Furthermore, for stunning selfies, the smartphone is equipped with an 8MP Front Camera.
vivo’s Y15C boasts a 5000mAh (TYP) battery that ensures plenty of life every day. A single full charge can provide up to 18.74 hours of online HD movie streaming, or 7.89 hours of intensive gameplay. It is also engineered to offer 5V/1A Reverse Charging, so your Y15C can be used to charge other devices, like a mobile power bank.
Immersive Display and Stylish Design
Y15C presents a 6.51-inch* Halo FullView™ Display with HD+ (1600×720) resolution to provide an immersive viewing experience to users while streaming videos, surfing the internet, and playing games. It is worth noting that the display’s brightness gets automatically adjusted based on the ambient conditions or surroundings. It does not stop there! Y15C also has a special Eye Protection Mode* that, when used, filters out harmful blue light to prevent eye strain for the user and keep the screen looking magnificent while remaining gentle on the eyes.
The impressive features are packed into a slender 8.28mm thin body with a 3D back cover. It is a lightweight handset offering a comfortable hold and smooth grip.
Dazzling Colours
vivo Y15C comes in two vivid hues to choose from: Mystic Blue and Wave Green.
Elevated Experience
Widely known for being a youth-centric brand, vivo has integrated several features to upgrade and enhance the youth’s experience and has customized the smartphone for the ‘On the Go’ generation.
Other Features:
The vivo Y15C runs on Funtouch OS 12 (Android 12) and comes with more special features that come in handy for day-to-day use:
Price and Availability
vivo Y15C is available for purchase across Pakistan at the price Rs. 31,999 only. vivo offers one-year warranty for vivo Y15C along with 15 days of free replacement and 6 months warranty for accessories. vivo Y15C is duly approved by Pakistan Telecommunications Authority and supports all mobile networks in Pakistan. Zong customers can also get 12GB Free Mobile Internet by using their 4G SIM card in Slot 1 (2GB Internet / month for 6 months).

Download
This is a Brookings Center on Regulation and Markets policy brief.
While there is little debate that digital forces are playing an increasingly crucial role in the economy, there is limited understanding of the importance of the digital infrastructure that underlies this role. Much of the discussion around digital infrastructure has focused on broadband availability (which is certainly important), but the role of free and open source software (FOSS or OSS) has gone underappreciated. FOSS—software whose source code is public, is often created by decentralized volunteers, and can be freely used and modified by anyone—has come to play a vital role in the modern economy. It is baked into technology we use every day (cars, phones, websites, etc.), as well as into various aspects of critical infrastructure including our finance and energy systems.
Like physical infrastructure, this digital infrastructure requires regular investment to further enable innovation, commerce, and a flourishing economy. However, also like physical infrastructure, there is a market failure in the private sector that leads to an underinvestment in digital infrastructure. Therefore, there is a clear need for government investment and regulation to ensure the future health, security, and growth of the FOSS ecosystem that has become indispensable to the modern economy.
In this article I lay out policy proposals based on my academic research and that of others, as well as policies that exist in other countries who are ahead of the United States on investing in this critical asset. I first discuss the overall challenge FOSS faces and the limits of existing policy in the U.S. (which are primarily focused on government usage of FOSS, not on investing in the FOSS ecosystem directly). Finally, I present 11 policy proposals separated into four domains of focus: creating an open source program office; measuring and understanding the FOSS ecosystem; enhancing the positive economic impact of FOSS; and securing the FOSS ecosystem. Although there is no silver bullet for guaranteeing the future health and growth of FOSS, these proposals will go a long way towards ensuring FOSS can continue to play its essential role in enabling the modern U.S. economy to grow and flourish.
At the highest level, the challenge related to FOSS is that despite its value to the modern economy, its decentralized and free nature leads to both an underappreciation of this value and an underinvestment in its growth and security.

Source: XKCD, https://xkcd.com/2347/, licensed under Creative Commons Attribution-NonCommercial 2.5 License
On the value side, although it has been estimated that up to 98% of codebases include FOSS, it can be difficult to measure its value. Traditional measures of the value of a product, such as multiplying the number of times a product is used times the price of the product and subtracting input costs, do not work. The price is zero, the labor is volunteered, and measuring the volume of usage is extremely difficult due to the distributed nature of FOSS and the fact that it can be copied and reused freely. Despite these challenges, there have been some recent efforts to value FOSS by myself and others. For example, our early efforts to measure the value of just one piece of FOSS—the widely used Apache web server—found that in 2013, it added up to $12 billion to the U.S. economy, despite not showing up directly in any GDP statistics. More recently, a European Commission sponsored report found that in 2018, EU companies invested roughly €1 billion into FOSS creation, which resulted in up to a €95 billion benefit for FOSS users in the EU. Similar estimates for the U.S. investment in FOSS were $33 billion in 2019. However, despite these attempts, we have only scratched the surface of truly understanding the value FOSS provides to the economy and modern life. This is even more so the case when considering the value created in the context of digital autonomy, as an increased reliance on FOSS can limit the occurrence of single points of failure where a company or country is beholden to a particular company that provides proprietary software or owns a patent (especially in the context of communications standards, like 5G).
Related Content


On the investment side, the challenge is twofold. First, despite increasing evidence for a high rate of return to public and private investment in FOSS that can enhance competitiveness and innovation, the U.S. has yet to make a concerted effort to directly invest in it—beyond just supporting its use in federal agencies. The U.S.’s investments in the Global Positioning System (GPS) is an example of the success such investments can have—U.S. investments in GPS, which is made freely available to users, have enabled $1.4 trillion of economic gains for U.S. companies (which the government receives tax revenue on). Likewise, our work on Apache showed that government investments in FOSS can lead to a rate of return of at least 17%, more than double the U.S. government’s commonly used baseline of 7% representing a good investment opportunity. Broader analysis in the European Commission report revealed a cost-benefit ratio of roughly 1:4 for FOSS investments by private companies, and my own work on government support of FOSS in France showed a variety of positive outcomes, including as much as an 18% increase in the founding of French IT-related startups and as much as a 14% increase in the number of French workers employed in IT-related jobs. Even for companies, my research has shown that not only does using FOSS lead to productivity gains but investment in FOSS can pay dividends as companies that contribute to FOSS obtain up to 100% more productive value from using FOSS than their free-riding peers.
Second, an underinvestment in FOSS can result in security concerns that have economy-wide consequences. The most recent evidence of this was the 2021 discovery of the Log4Shell vulnerability in the FOSS logging package log4j. Deployed across a vast range of digital applications, the vulnerability was originally introduced in the code in 2013 and exposed tens of millions of devices to a devastating security vulnerability and illustrated the urgent need to improve security in open source software. Jen Easterly, the director of the United States Department of Homeland Security (DHS) Cybersecurity and Infrastructure Security Agency (CISA) called Log4Shell “the most serious vulnerability I’ve seen in my decades-long career,” and well before most organizations could patch the vulnerability, there were over 800,000 attacks using it in a 72-hour period, including some by Chinese and Iranian government-sponsored actors. Government policy can help identify and address these vulnerabilities in a timelier fashion.
The biggest limit to existing U.S. policies related to FOSS is that they are nearly all focused on the federal government’s use of, creation of, and purchasing of technology for its own systems. No policies are targeted at measuring, investing in, or securing the FOSS ecosystem as a whole or in a direct manner. Although my prior research has shown that governmental policies favoring the usage of FOSS in technology procurement can have important positive spillovers to a country (as well as cost savings), this is more of a second-order impact rather than the first-order impact direct investment can have. There are numerous examples of such procurement policies. As early as 2004, agencies of the U.S. federal government started to clarify their stances towards FOSS. However, it was not until the Office of Management and Budget memorandum M-16-21 in 2016 that a clearer pro-FOSS stance was taken. M-16-21 required that all federal agencies should a) make all new custom code for any federal agency available for reuse across all federal agencies, and b) release at least 20 percent of new custom code as FOSS for anyone to use. These efforts were coordinated through the Code.gov website, originally developed under the Office of the Federal Chief Information Officer and now administered by the U.S. General Services Administration (although recently defunded and essentially static). To this day, M-16-21 is the primary guidance on how federal agencies should approach FOSS and is the primary authority cited within numerous agencies related to their FOSS stance (e.g., Department of Commerce and Department of Defense). These efforts were expanded upon with the May 2021 White House Executive Order 14028, which included a section requiring all federal government software purchases to include a software bill of materials (SBOM) that clearly stated what other software (including FOSS) was built into the purchased software.
Beyond M-16-21, a handful of other governmental efforts have been proposed but not passed. For example, the House version of the 2022 National Defense Authorization Act included funding for a FOSS security center within DHS, but the funding did not make it into the final bill. At the state level, New York has introduced a bill to give a tax credit for expenses related to developing FOSS in every legislative session since 2009, but the bill has never gotten out of committee. Even the much-praised bipartisan infrastructure package passed in late 2021 focused its digital infrastructure investments nearly exclusively on broadband availability and did not address investments in FOSS.
Most recently, in January 2022, in response to the aforementioned Log4Shell vulnerability, the White House National Security Council (NSC) held a meeting with companies like Google and Microsoft; open-source organizations including the Linux Foundation, the Apache Software Foundation, and the Open Source Security Foundation (OpenSSF); and numerous federal agencies and departments. The meeting focused on preventing, finding, and shortening response time to FOSS vulnerabilities and discussed various potential public-private partnerships. Although there were no concrete pledges from the meeting, the intent was to start a discussion, identify possible paths forward, and commit to future meetings that would yield specific commitments by the various stakeholders. In May of 2022, the first follow-up meeting was held and it identified 10 areas of focus to improve OSS security and provided specific plans of action and a call for $150 million in funding over two years. The intent was for this funding to come from private companies, not the government, and some large tech companies have already committed $30 million to assist in the effort.
Given the lack of federal policies directly supporting the FOSS ecosystem, I lay out 11 policy proposals that can help to support the FOSS ecosystem in critical ways (overviewed in Table 1). These policies are grouped into four domains. The first domain is to create a new office to oversee all FOSS related activity within the federal government. The second domain focuses on measuring and understanding the FOSS ecosystem, which is necessary given the distributed nature of FOSS, and the lack of a clear understanding of how pervasive it is in the modern economy. The third domain considers avenues for investing in FOSS to help enhance the economic competitiveness of the U.S. The fourth domain focuses on methods for securing existing and future FOSS to reduce the likelihood of some of the issues mentioned above. Some of the policy recommendations build upon the European Commission report mentioned above, for which I was an outside advisor, but consider how (and where) they could be applied in the U.S. Further, although all of these recommendations are focused on FOSS, they can be thought of to include free and open source hardware as well, which is a smaller space than FOSS but is rapidly growing and is increasingly important to the economy.
Table 1: Recommendations for Strengthening Digital Infrastructure

source